 StorageDigital Storage ForensicsHDD ForensicsImage hard drives through a write-blocker, find hidden areas and recover deleted data.
Exterro
Exterro FTK Imager
FTK Imager is the free tool most learners meet first. It makes forensic images of drives, folders and memory, verifies them with hashes and lets an examiner preview evidence before committing to a full acquisition.
UtilityFreeCurrentWindows
Profile
- Manufacturer
- Exterro
- Category
- Computer forensics
- Product type
- Utility
- Platforms
- Windows
- Licensing
- Free
- Product status
- Current
- Educational level
- Beginner
- Last verified
- 2 November 2026
Exterro's page calls the product Exterro FTK Imager and states that it is free. The page does not name image formats or a version. FTK Imager Pro is a separate paid product listed on the same site. Windows comes from the page's structured data rather than its visible text.
What Exterro FTK Imager is
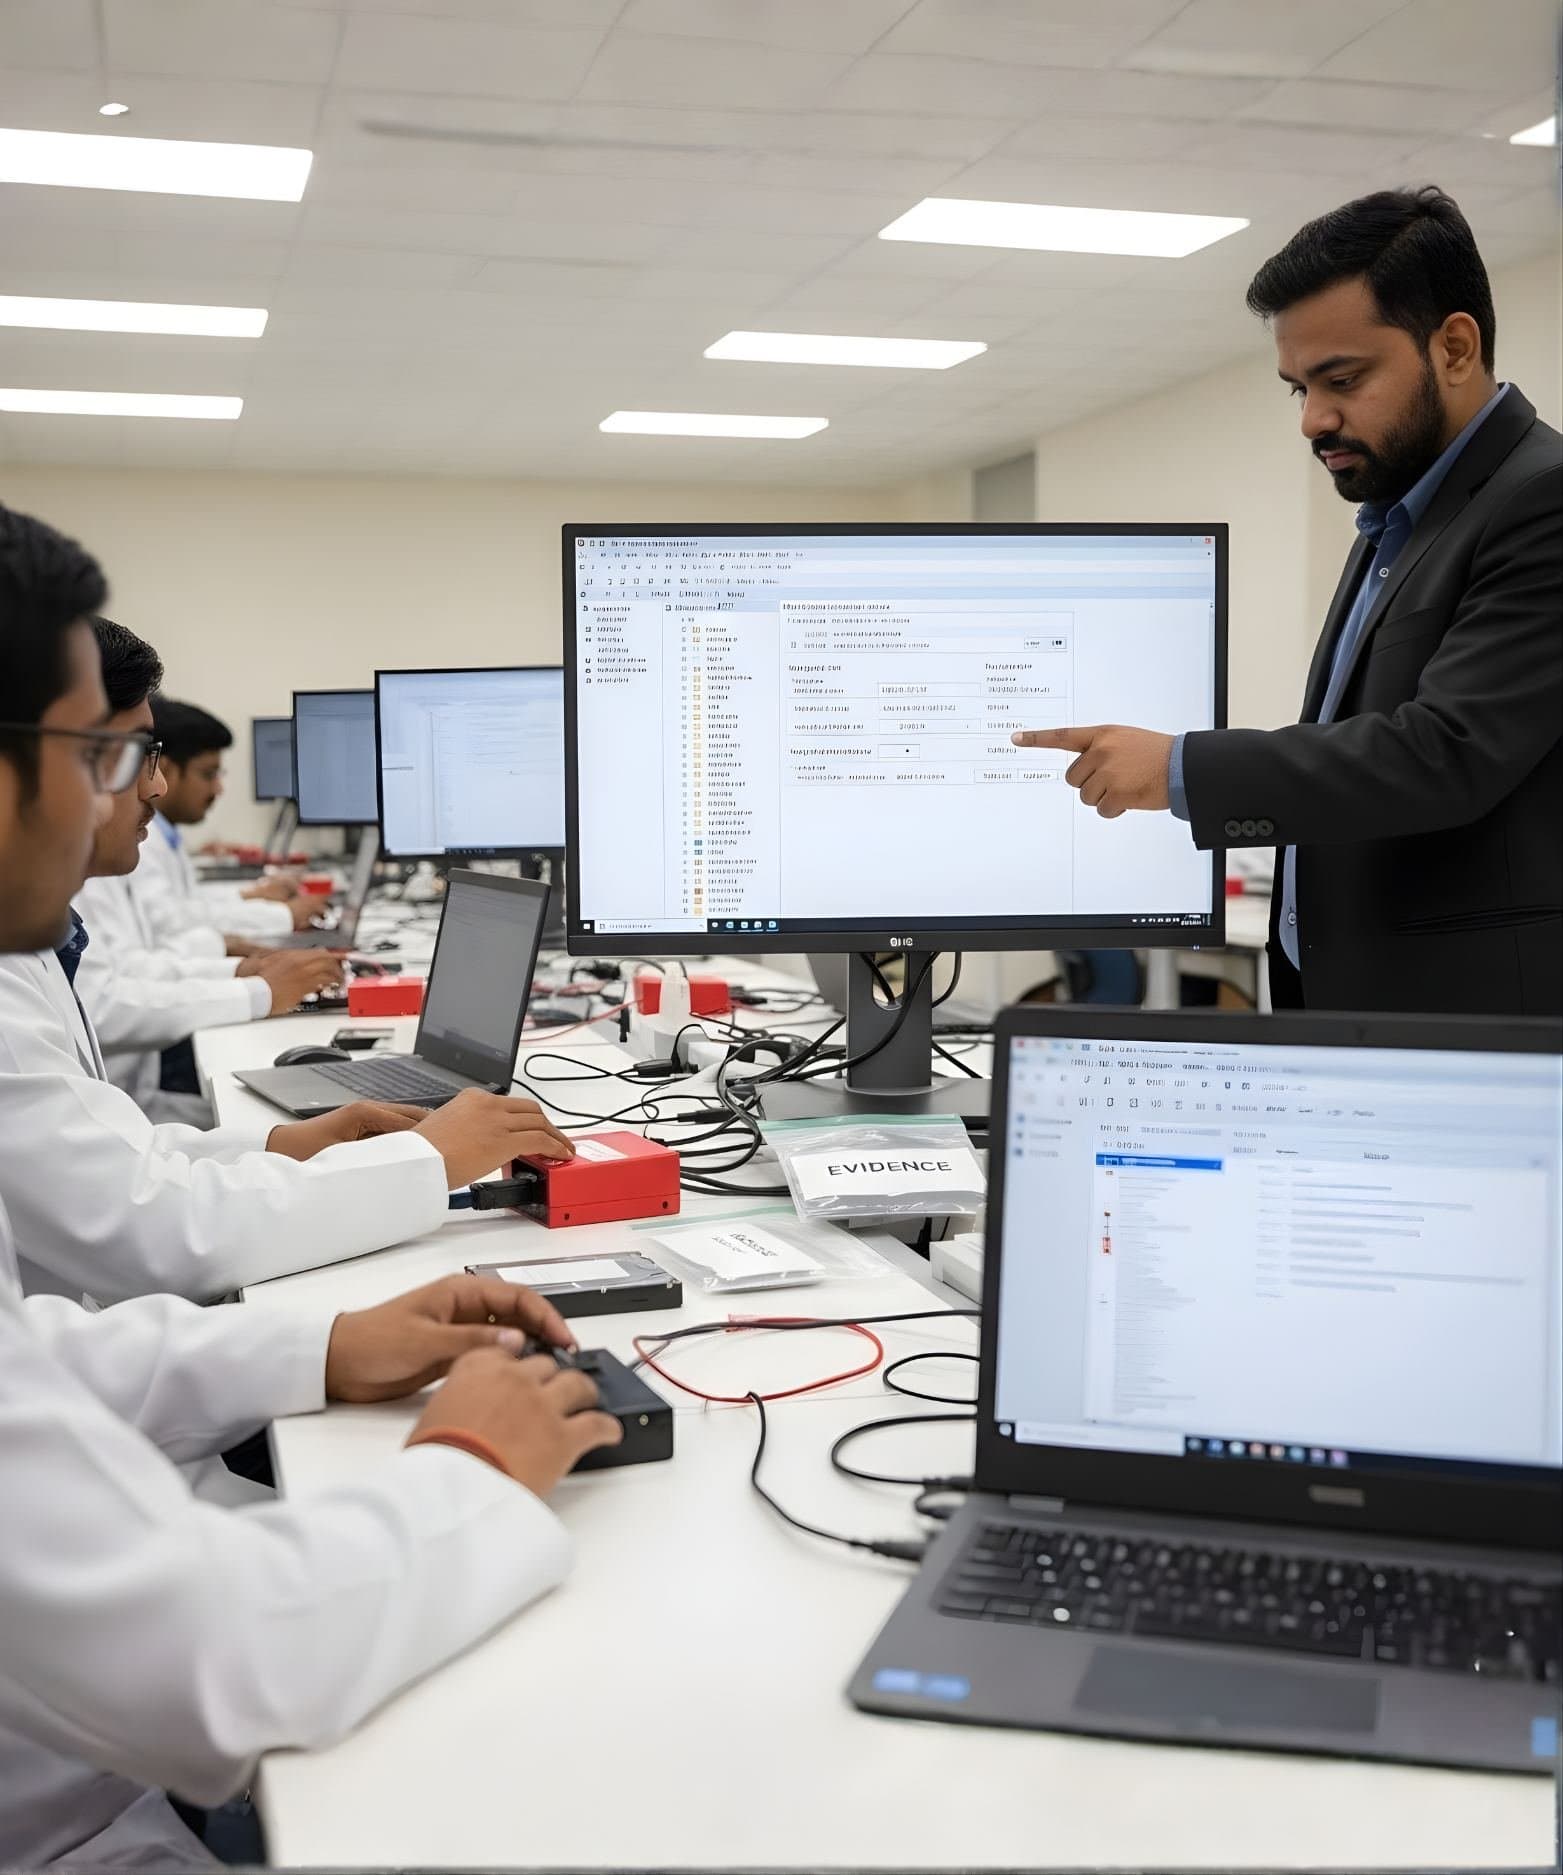
Every image starts somewhere. In Indian classrooms and small labs it often starts with FTK Imager. Exterro gives it away. The tool reads a physical drive, a logical volume, a folder or an existing image, shows the file system tree and lets the examiner look inside files without changing them. From there it can write a full image, capture live system memory before a machine is powered down or export selected files. Hashes are calculated during the copy and checked after it. The tool writes a report of the job with those values, which becomes part of the case file.
Exterro's page says it captures disk images, files and memory and supports common forensic image formats, without listing them. It also now sells a separate paid product, FTK Imager Pro, which adds iOS advanced logical collection, detection and decryption of BitLocker and similar encryption using known credentials and direct access to live decrypted data. Learners should keep the two apart: the free tool is still the free tool. What FTK Imager does not do is protect the source drive from writes on its own. A hardware write blocker or a verified software method must sit between the evidence and the computer.
Primary applications
Where it is used
- Creating a forensic image of a hard drive, SSD or USB stick
- Previewing a drive or image to decide whether a full acquisition is needed
- Capturing live memory from a running system
- Exporting selected files and folders from an image with their hashes
- Verifying that an image matches its recorded hash values
Who uses it
- Students and new trainees
- First responders who image before handing over to a lab
- Examiners verifying images made by others
- IT staff collecting evidence under instruction
Capabilities and limits
Major capabilities
- Imaging of physical drives, logical volumes and folders
- Preview of files and folders inside a drive or image before acquisition
- Live system memory capture
- Hash verification of every acquisition with a written report
- Support for common forensic image formats, as stated by Exterro without naming them
- Free download from Exterro
- Windows platform, as given in the page's structured data
Technical limitations
- It is an acquisition and preview tool; analysis needs FTK or another examination tool
- It does not block writes to the evidence drive; a write blocker is still needed
- Encrypted volumes need credentials and the decryption features are sold separately in FTK Imager Pro
- Exterro's page does not list the image formats or the current version
- Memory capture changes the live system, so the order of actions must be recorded
Learning with DFRTI
Independent professional education covering the principles and workflows of Exterro FTK Imager. DFRTI is not a vendor training centre and its courses are not vendor certifications.
Before you learn it
- What a bit-for-bit image is and why a hash proves it
- Write blocking and the order of volatility
Disciplines
Related tools
- Exterro FTK Forensic ToolkitFTK is the Forensic Toolkit that AccessData built and Exterro has owned since late 2020. Today Exterro sells it as Exterro FTK in a standalone form and as FTK Central for teams, with FTK Imager alongside.Exterro
- OpenText Forensic (EnCase)EnCase Forensic, one of the oldest names in computer forensics, is now called OpenText Forensic (EnCase). OpenText says it is the same product, renamed to fit its cybersecurity portfolio.OpenText
- Arsenal Image MounterArsenal Image Mounter, or AIM, mounts a disk image in Windows as a complete disk rather than a share, so Windows itself sees partitions, shadow copies and BitLocker volumes. The free mode covers mounting; Professional Mode adds virtual machine launch and more.Arsenal Recon
- Hardware Write BlockersA hardware write blocker sits between an evidence drive and the examiner's computer and refuses every write command. It is the first device a new examiner should understand.Various manufacturers
- Forensic DuplicatorsA forensic duplicator is a standalone imaging device. It copies a source drive to a destination drive or image file, hashes the result and verifies it, without a computer in between.Various manufacturers
- Magnet ACQUIREMagnet ACQUIRE was Magnet Forensics' free acquisition tool for Android and iOS devices, later extended to computers. It no longer appears on Magnet's product or free tools pages. Its acquisition engine now lives inside Magnet Axiom.Magnet Forensics
Courses that cover this tool
StorageDigital Storage ForensicsHDD ForensicsImage hard drives through a write-blocker, find hidden areas and recover deleted data. StorageDigital Storage ForensicsUSB / Pen Drive ForensicsExamine pen drives and memory sticks and prove which USB device touched which computer.
 MalwareIncident Response & Malware AnalysisMemory ForensicsCapture RAM and use Volatility 3 to find hidden processes, injected code and connections.
 LegalFoundation & Legal CoursesBasics of Cyber ForensicsStart here. Evidence handling, imaging, hashing, chain of custody and your first analysis.
Related reading
- SSDs, TRIM and What Happens to Deleted DataOn a hard disk a deleted file usually sits where it was until something overwrites it. On an SSD the drive itself may clear it within minutes. This explainer covers TRIM, garbage collection and wear levelling, what a forensic image of an SSD really contains and why file carving so often comes back empty.Explainer
- Hash Verification in Digital EvidenceA hash value is the one number that lets a court trust that the copy examined is the copy seized. This tutorial covers which algorithms to use and why, when to hash, how hash sets work, how to verify an image against its source and how to write hashes into the chain of custody and the report, with a worked synthetic example.Technical tutorial
Official source
Product names and trademarks belong to their respective owners. DFRTI is an independent educational and research institute. Inclusion in this directory does not imply manufacturer endorsement, partnership or authorisation. Facts are checked against the manufacturer's public documentation on the date shown and may have changed since.
Go deeper with DFRTI
Free pages explain the ground. Structured courses, lab work and a mentor take you from knowing about it to doing it on a case.